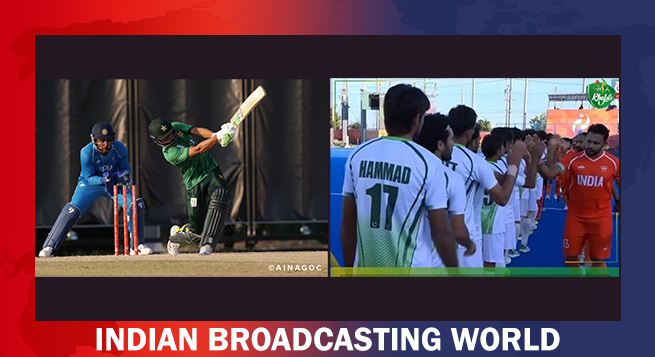
 Ind, Pak cricket & hockey matches most viewed in Asian Games history
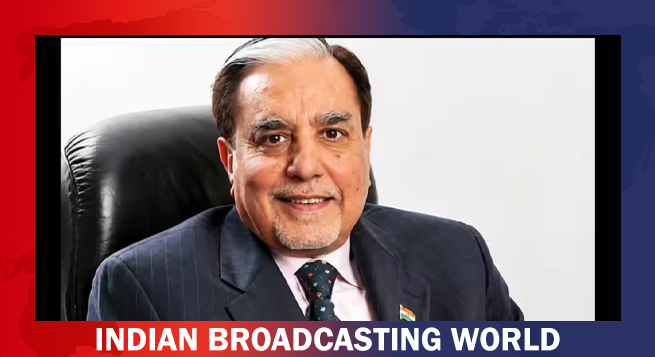 Zee completes 34 years as Subhash Chandra recalls media journey
 Ficci FRAMES session discusses what makes reality TV tick
 Shekhawat: India must shift from content consumer to global creator
 Puneet Goenka, Gaurav Banerjee, Rahul Kanwal share views on TV ratings
 Doordarshan seeks agency for DD Free Dish auctions
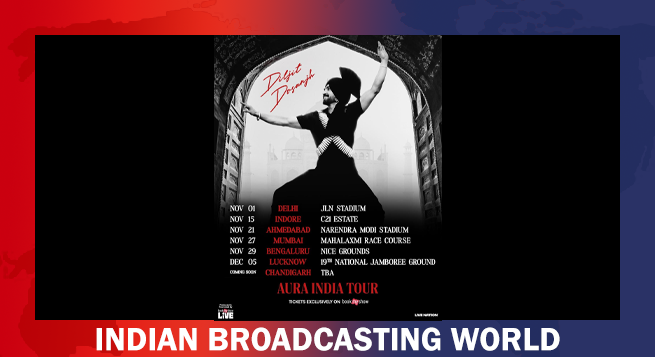 Diljit Dosanjh announces India dates for Aura Tour
 Prime Video unveils trailer for ‘Ishqa Ishqa’
 Ayushmann’s tribute takes Big B back to ‘Kabhi Kabhie’, ‘Deewaar’
 Sony LIV’s Malayalam Original ‘EYES’ to premiere on Oct 9

Meta yesterday removed dozens of advertisements after India flagged a pattern of Facebook and Instagram ads using sexually explicit content to lure users into downloading malware that could steal banking credentials and drain bank accounts.
According to a Reuters report from Bengaluru yesterday, India recorded nearly $2.4 billion in cyber-fraud losses in 2025, government data shows, as scam operators increasingly target the country’s digital-payments boom.
The government, according to the Reuters report, said ads on Facebook and Instagram operating under names such as ‘Night Play’ and ‘Kyss’ directed users to phishing websites.
It said it had observed a rise in financial fraud involving what it described as “malicious Android applications masquerading as pornography apps”.
Reuters found at least 39 such ads still active after the government advisory was issued on Monday, with many of them using sexually explicit video thumbnails to attract clicks.
Meta took down all of the ads shortly after Reuters flagged them to the company, seeking comment on the advisory. Meta did not respond to Reuters queries.
Reuters is first to report Meta’s removal of the ads following the government advisory.
The US technology giant’s policies state that ads “must not contain adult nudity and sexual activity”. They also prohibit ads for “products, services, schemes or offers using identified deceptive or misleading practices”, including those intended to scam users out of money.
It is the second time in recent weeks that India has raised concerns about financial fraud on a major technology platform.
Reuters previously reported that the government directed Google to shut down hundreds of accounts on its Firebase platform after finding criminals were using the service to impersonate major banks.
Meta had internally projected that scam and banned goods advertising would generate about 10 percent of its 2024 revenue, or roughly $16 billion, even as the company says it is cracking down on such ads, Reuters reported last year.
One ad, while still active, led to a website promoting a video app that promised hundreds of pornographic videos and round-the-clock content. Access required users to directly download a file named ‘Movexa.apk’ outside an official app store.
India’s advisory said the apps could secretly access information stored on users’ phones, capture one-time passwords and bank PINs, and transfer money from accounts without the owner’s knowledge.