 Akash Ambani banks on selling more services to up revenue
 Sunil Mittal says OneWeb ahead of Musk in Indian approval queue
 Murugan resigns from Cabinet as Mos MIB & Rajya Sabha
 Broadcasters flag HD-SD conversion, satellite spectrum concerns in submission to MIB on telecom rules 2026
 MIB seeks dismissal of AIDCF plea against WAVES, says OTT rules differ from TV
 Lilly Singh returns to YouTube, puts creative freedom over Hollywood
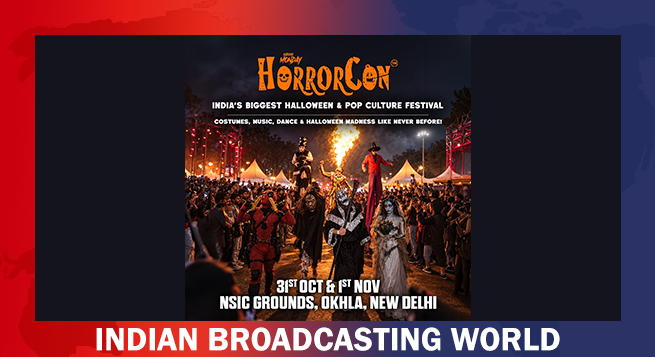 HorrorCon India to bring hip-hop duo Seedhe Maut, other attractions
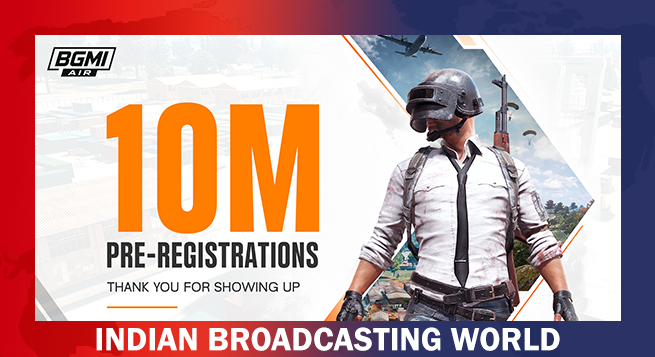 BGMI Lite renamed BGMI Air as pre-registrations cross 10mn
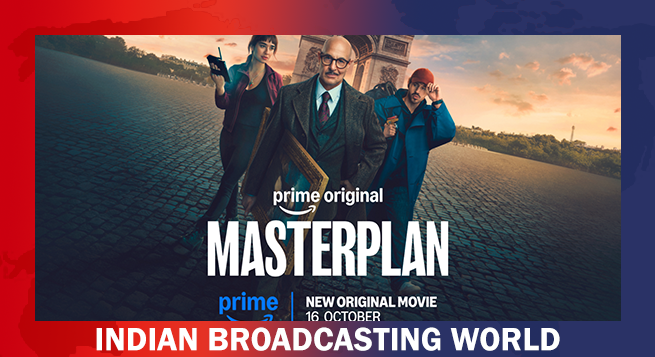 Prime Video starts streaming ‘Masterplan’ starring Stanley Tucci
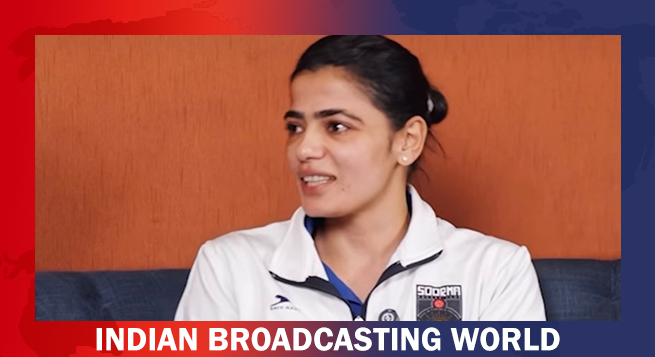 Hockey legend Savita Punia wants Priyanka to essay her in biopic

More than a dozen malicious India-linked domains and websites that were being used in attacks targeting users worldwide by hack-for-hire groups have now been banned by American tech giant Google’s Threat Analysis Group (TAG).
To warn users about the threat, the company recently published a blog post where they listed these banned domain links which used to inject spying tools into users’ PCs/laptops by appearing as fake login pages for websites or apps, ANI reported.
The blog post read, “As part of TAG’s mission to counter serious threats to Google and our users, we’ve published analysis on a range of persistent threats including government-backed attackers, commercial surveillance vendors, and serious criminal operators.”
“We’re sharing intelligence on a segment of attackers we call hack-for-hire, whose niche focuses on compromising accounts and exfiltrating data as a service,” it continued.
Whenever a user typed in their login credentials on these domains, their details were secretly sent to the hacker, who could then use them to break into the user’s system and take complete control over it. Government organizations to AWS and Gmail accounts have been the targets of these phishing messages.